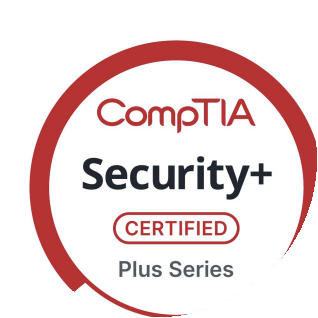
CompTIA Security+ ce
Valid through August 31, 2029Issued August 31, 2026 · John Calvin Tyler
561761119d6a4f25b92bf9ea30f18233Verify with CompTIAIAM and cloud security professional focused on Microsoft Entra ID, Azure, identity governance, and privileged access.
I build hands-on identity and cloud security projects using RBAC, Conditional Access, PIM, PowerShell, and security automation.
ABOUT
I’m an IT and cybersecurity professional with a background in technical support, identity lifecycle support, and access control. My work at VIP Access Management (2021–2023) involved employee, contractor, and visitor credentials, approved access requests and deactivation, access logs, and audit documentation.
As an IT Support Specialist at Oatridge (2023–2026), I supported Windows and Microsoft 365 environments, including Active Directory and Entra ID provisioning and deprovisioning, password and MFA support, groups, access changes, and account and authentication troubleshooting. I used ServiceNow and PowerShell diagnostics to investigate user issues.
My current direction is cloud, IAM, and automation. Through hands-on labs and public projects—not employer production deployments—I explore Conditional Access, PIM/JIT, Azure RBAC governance, Graph PowerShell, an Entra-authenticated web console, and enterprise Azure infrastructure. I document what I learn and build practical tools and repeatable workflows.
PROFESSIONAL CERTIFICATIONS
Open CompTIA’s official verification page, then enter John Calvin Tyler and the verification code shown on the credential.
Issued August 31, 2026 · John Calvin Tyler
561761119d6a4f25b92bf9ea30f18233Verify with CompTIA
Issued June 17, 2026 · John Calvin Tyler
9dfdc8ff493643b8a3786c8cafcb9552Verify with CompTIAEXPERTISE
A practical skill set developed through production support, security operations, structured study, and hands-on technical environments.
Identity lifecycle, access controls, account governance, Microsoft Entra ID, and Active Directory.
Cloud engineering, cloud identity, tenant administration, access configuration, and secure operating practices.
Windows Server, endpoint troubleshooting, Group Policy, virtualization, and reliable systems support.
Hands-on detection, log analysis, Splunk workflows, incident triage, and vulnerability management.
Repeatable scripts that reduce manual work, improve consistency, and support technical investigations.
Core TCP/IP, DNS, DHCP, routing, segmentation, connectivity analysis, and lab-based troubleshooting.
Clear diagnosis, user-focused communication, documentation, escalation, and durable problem resolution.
Practical web tools and SaaS concepts designed around real security and operational workflows.
FEATURED PROJECTS
Hands-on projects in cloud engineering, identity and access management, cybersecurity, systems administration, and automation—documented through labs, tools, and technical walkthroughs.
Showing all 18 projects
Cloud infrastructure, Entra identity governance, access lifecycle, and repeatable Azure delivery.
ZERO TRUST & PRIVILEGED ACCESS
AZURE IDENTITY GOVERNANCE
AZURE IDENTITY & ACCESS LIFECYCLE
AZURE CLOUD ADMINISTRATION
CLOUD IDENTITY AUTOMATION
AZURE CLOUD DELIVERY & CI/CD
AZURE CLI RESOURCE LIFECYCLE
AZURE PIM JUST-IN-TIME ACCESS
Security monitoring, threat triage, preparedness, and practical cybersecurity learning tools.
SIEM & SECURITY MONITORING
Built and configured a Splunk-based SOC monitoring environment using Windows Security Logs and Sysmon telemetry to investigate authentication activity, process execution, PowerShell activity, security events, and potential threat indicators through centralized dashboards and analysis workflows.
Centralized Windows telemetry
Windows Security Logs and Sysmon telemetry brought together for investigation.
Authentication activity
Review sign-in activity and authentication-related security events.
Process & PowerShell analysis
Inspect process execution and PowerShell activity for potential threat indicators.
SOC monitoring dashboards
Centralized dashboards support log analysis and security investigation workflows.
POWERSHELL & WINDOWS SECURITY
A PowerShell assessment tool that performs 31 read-only Windows security checks and generates an interactive HTML dashboard with endpoint posture scores, prioritized remediation guidance, Windows security event summaries, and security awareness training.
Read-only security assessment
Checks Microsoft Defender, Windows Firewall, BitLocker, SMB, logging, and other endpoint controls.
Prioritized findings
Scores security posture and organizes findings with severity, evidence, and remediation recommendations.
Windows security signals
Summarizes failed logons, account lockouts, process creation, and Defender detections.
Security awareness
Includes a user guidance playbook and interactive knowledge check.
LOCAL EMAIL TRIAGE
PhishLens is a local browser-based tool for inspecting suspicious emails, sender-domain mismatches, URLs, and attachment filenames, with explainable risk signals and evidence reports. An optional PowerShell launcher opens the app; email analysis runs in the browser.
CYBERSECURITY LEARNING TOOL
A browser-based CompTIA Security+ SY0-701 study dashboard with original scenario-based questions, flashcards, acronym and ports review, domain accuracy tracking, missed-question review, and local progress storage. Created for aspiring cybersecurity professionals.
Endpoint diagnostics, server administration, access control, and service desk workflows.
POWERSHELL DIAGNOSTICS
A PowerShell-based troubleshooting toolkit that automates Windows system health, network connectivity, Microsoft Defender, firewall, service, and event-log checks, with structured HTML reporting to speed up endpoint diagnosis and support workflows.
LINUX SERVER ADMINISTRATION
A hands-on Ubuntu Linux administration lab demonstrating remote server management over SSH, package management, Nginx deployment, systemd service administration, HTTP/HTTPS configuration, SSL/TLS certificate setup, configuration validation, and troubleshooting in a virtualized environment. Includes a Bash automation workflow for repeatable deployment.
IDENTITY & ACCESS CONTROL
Built a Windows domain access-control environment using Active Directory users, security groups, NTFS permissions, and network-share permissions to implement and validate group-based least-privilege access to organizational resources.
IT SERVICE MANAGEMENT
A simulated enterprise IT service management and help desk platform that connects Active Directory users, departments, tickets, and assets inside a realistic service desk environment. Demonstrates ticket assignment and escalation, asset tracking, role-based technician/admin access, password reset and account unlock workflows, troubleshooting documentation, and day-to-day IT operations.
Public technical work and hands-on technology education.
OPEN TECHNICAL PORTFOLIO
A growing portfolio of hands-on IT and cybersecurity projects spanning IAM, Microsoft Entra ID, Windows and Linux administration, security monitoring, PowerShell automation, ITSM, phishing analysis, and security tooling. Includes 25+ documented labs, browser-based security applications, diagnostic utilities, and practical projects built around real-world infrastructure and security workflows.
Documented labs
Active Directory, Entra ID, Windows Server, Linux, Splunk, networking, and PowerShell.
Cloud deployment work
Azure administration and Static Web Apps CI/CD projects with documented verification.
Security applications
PhishLens email analysis and a browser-based Security+ study dashboard.
Operational tooling
Windows diagnostics, ITSM workflows, automation playbooks, and practical support documentation.
TECHNICAL EDUCATION CHANNEL
A hands-on IT and cybersecurity channel documenting practical labs, real-world administration, troubleshooting, automation, and technical education across Microsoft Entra ID, Azure, PowerShell, Windows Server, Linux, networking, IAM, cloud infrastructure, and security operations.
Cloud & identity walkthroughs
Microsoft Entra ID, Azure administration, IAM, and cloud infrastructure labs.
Systems administration
Hands-on Windows Server and Linux configuration, networking, and troubleshooting.
PowerShell & automation
Practical scripting and repeatable workflows for administration and technical support.
Cybersecurity education
Security operations labs and technical explanations grounded in hands-on practice.
PROJECT WALKTHROUGH
A hands-on walkthrough of my Azure Identity Governance Console, combining Microsoft Entra ID identities and Azure RBAC assignments to trace a user's effective access. The demo follows Michael Chen's Identity 360 view, Finance group membership, and authorization paths, then validates access in the Azure Portal.
INTERACTIVE IAM & SECURITY TRAINING LAB
CyberOps Triage Lab
CyberOps Triage Lab is a browser-based hands-on training environment built for IT support, IAM, and cybersecurity professionals to practice realistic identity, access, cloud, and security decision-making in a safe simulated environment.
Built for practice and skill development—not a production security platform. Scenarios use fictional evidence; no production systems or cloud tenant are connected.
YOUR OPERATIONS OVERVIEW
Welcome to the lab.
Investigate the evidence. Make the right call.
Investigation queue
Impossible travel, familiar device
Microsoft Defender · SOC
A wave of password failures
Microsoft Defender · SOC
PowerShell on a finance workstation
Microsoft Defender · SOC
Fictional data. Real decision-making. Progress stays in your browser.
FREE SECURITY+ STUDY RESOURCE
A study resource I built for aspiring cybersecurity professionals pursuing CompTIA Security+. Practice key concepts, review what you miss, and build a consistent study routine with questions, quick references, and progress tracking in one place.
Independent study resource by John Tyler. No account required; progress stays in your browser.
Scenario practice
Work through original questions with immediate explanations.
Flashcards & quick references
Review security concepts, acronyms, and common ports and protocols.
Domain progress
Track accuracy across study domains to see where to focus next.
Missed-question review
Revisit incorrect answers in a dedicated review queue.
EXPERIENCE & DIRECTION
My path has progressed from security operations and access control into IT support, systems troubleshooting, and identity lifecycle support. I’m now deepening my cloud, IAM, and automation skills through hands-on labs and public technical projects.
OATRIDGE · SUPPORT SCOPE
Supported 30+ Windows endpoints and over 200 Microsoft 365 users across headquarters and client sites, resolving identity, application, and connectivity issues.
2021–2023 · VIP ACCESS MANAGEMENT
Supported employee, contractor, and visitor credentials, approved access requests and deactivation, access logs, and audit documentation.
2023–2026 · OATRIDGE
Supported AD and Entra identity lifecycle provisioning and deprovisioning, password and MFA issues, groups, access changes, and account and authentication troubleshooting, using ServiceNow and PowerShell diagnostics.
CURRENT DIRECTION · LABS & PROJECTS
Developing advanced Conditional Access, PIM/JIT, Azure RBAC governance, Graph PowerShell, Entra-authenticated web console, and enterprise Azure infrastructure skills through hands-on labs and projects—not employer production deployments.
WHAT I’M BUILDING
VENTURES & PRODUCTS
Building technology-driven products across cybersecurity, financial systems, and long-term value creation.
CYBERSECURITY GOVERNANCE & RISK PLATFORM
Praevyn is a cybersecurity governance platform built to transform complex security risk into clear, defensible decisions—combining maturity assessment, exposure management, remediation tracking, and compliance oversight in one system.
PROFESSIONAL OPPORTUNITIES
Open to IAM, Microsoft Entra ID, cloud identity, Azure administration, and cloud security opportunities.
GET IN TOUCH
Tell me what you’re working on, the problem you need solved, or the opportunity you’d like to discuss.